CybersecurityBuiltfortheWayAfricaGetsAttacked
FortiGate Perimeter | Endpoint Protection | Incident Response
National KE-CIRT/CC detected over 4.5 billion cyber-threat events in Kenya from October to December 2025. 912 addresses exposure across identity, network segmentation, perimeter controls, and endpoints. The FortiGate and FortiAnalyzer architecture shown here was deployed end-to-end for a Kenyan manufacturer.
Request Consultation
Technologies in use
Evidence, not promises.
See how clients improved resilience, visibility, and operational control with 912.
FortiGate + FortiAnalyzer — Kenyan manufacturer
FortiGate 121G with SP5 hardware acceleration and a FortiAnalyzer VM deployed end-to-end — 3-year licence bundle and six months of configuration support.
Read the case studyFull TCO quoted before signature
The engagement quote stated the deployment fee, licence term, and the ~USD 4,000 renewal OPEX after year three — total cost of ownership on the table up front.
Read the case studyCrisis incident response — factory rescue
An enterprise recovered mid-crisis: triage, containment, full data restoration, and rebuilt operating documentation under live operational pressure.
Read the case studyWhen this service becomes urgent
912 builds cybersecurity around distinct operating layers: Bitdefender GravityZone endpoint protection, FortiGate perimeter controls, identity hardening, VPN discipline, recovery, and incident readiness. Each control has a stated owner, support window, and limit.
Discovery call agenda
Firewall and endpoint baseline (FortiGate + Bitdefender GravityZone), policy cleanup, vulnerability review, identity hardening, EDR alert routing, monitoring cadence, and incident-response escalation.
- 1Review current firewall, endpoint tool, and EDR coverage.
- 2Identify top exposure paths and compliance pressure (ODPC, CBK, PCI-DSS).
- 3Define remediation sprint or Security Shield retainer scope.
What the numbers say about leaving this alone
The question is not whether your perimeter gets probed. It is whether anyone would notice, and how long the gap between the breach and the discovery would run.
National KE-CIRT/CC detected 68,726,238 malware threats and 12,115,001 web-application attacks in Kenya during Q3 FY2025–26.
Communications Authority of Kenya / National KE-CIRT/CC(opens in a new tab) — threats detected in Kenya, Q3 FY2025-26
In Serianu’s Kenya research, 37% of surveyed organisations experienced a cyber incident in the previous year and 35% rated their resilience as low.
Serianu(opens in a new tab) — Africa Cybersecurity Report — Kenya
IBM’s Cost of a Data Breach study reported a mean time of 247 days to identify and contain a breach.
IBM — in IBM's own Cost of a Data Breach study
Enterprise Defense Architectures
Hardware-Accelerated Perimeter
- SSL/TLS inspection at wire speed
- 18× GE ports + 10GE SFP+ uplinks, dual power supplies
- 480GB onboard storage for local logging and forensics
Centralized Intelligence
- Centralized log aggregation across the estate
- Security analytics and compliance reporting
- An audit trail that survives the device that generated it
Zero-Trust & Identity
- Active Directory / LDAP integration
- Time-based access restrictions
- 2FA / MFA enforced at the edge
The Reality of Kenyan Cybersecurity
Over 4.5 billion cyber-threat events detected in Kenya from October to December 2025 (National KE-CIRT/CC).
Legacy firewall and remote-access configurations that have not been reviewed.
Fragmented security tools that don't communicate with each other.
Lack of specialized incident response talent in-house.
Honest Risk Framing
What this protects against — and what it doesn't.
Support covers our configurations, not yours
Post-deployment support covers the rules, policies, and configurations 912 deployed. Major new requirements introduced by your team after handover — new VPN endpoints, new VLAN segments, new SaaS integrations — require a separate scoping engagement.
Endpoint pricing depends on device counts and tier
Endpoint protection (Bitdefender GravityZone) is licensed per device, and the tier matters: not every business needs full EDR. We size the recommendation to your actual risk — not every business needs Enterprise — and surface licence cost transparently so renewals aren't a surprise.
User behavior is outside the firewall's scope
FortiGate can block phishing payloads at the perimeter and GravityZone can isolate compromised endpoints, but neither stops a user voluntarily approving an MFA prompt. Cybersecurity Training engagements layer human-factor mitigation on top of the technical stack.
How a Deployment Actually Runs
The same shape as our delivered FortiGate engagement — including the honest parts most vendors leave off the quote.
Part of the 912 six-phase engagement model — this is how it runs for this service.
Audit & Specification
Baseline the current firewall, endpoint, and identity stack. Specify the right appliance for your throughput — with the full cost on the table: licence term, deployment fee, and the renewal OPEX three years out.
Procurement & Staging
Honest delivery windows quoted up front — enterprise firewall hardware typically runs about six weeks; virtual appliances like FortiAnalyzer land in days. Configuration is staged while hardware ships.
Deployment & Policy Build
Install, segment the network, build the security policies, integrate identity (AD/LDAP, MFA), and wire all telemetry into FortiAnalyzer.
Support & Handover
Six months of support on every configuration 912 deploys — security policies and network management included — plus documented policies your team can audit. Ongoing monitoring is available as a separate retainer.
Why 912
Deployed, Not Just Specified
The FortiGate + FortiAnalyzer architecture on this page isn't a brochure diagram — it was deployed end-to-end for a Kenyan manufacturer.
TCO on the Table
Our firewall quotes state the deployment fee, the licence term, and the post-licence renewal cost before you sign — because a perimeter you can't afford to renew in year four is a security incident on a timer.
Layers That Match the Threat
Perimeter (FortiGate), endpoint (Bitdefender GravityZone — independently verified to detect 100% of MITRE ATT&CK attack steps for three straight years), and the human layer (security training) — each covers what the others can't. We're explicit about which layer stops which attack, and which tier of GravityZone your risk profile actually needs.
Compare the deployment model, operating work, lifecycle, prerequisites, and where another option may be the better fit before selecting a product.
Executive Intelligence
How does 912 secure a Kenyan enterprise network?
With layered, identity-centric architecture: a hardware-accelerated FortiGate perimeter performing SSL/TLS inspection, VLAN segmentation so a breach in one zone can't roam the estate, MFA enforced on administrative and remote access, Bitdefender GravityZone on the endpoints, and all telemetry centralized in FortiAnalyzer for analysis and compliance reporting. 912 deployed this architecture end-to-end for a Kenyan manufacturer, with six months of configuration support included after deployment.
From the Delivered Engagement
FortiGate 121G + FortiAnalyzer VM, deployed for a Kenyan manufacturer.
Fortinet
Technology in scope
Bitdefender GravityZone
Technology in scope
Cisco
Technology in scope
Microsoft Security
Technology in scope
Common Questions
Everything you need to know about Cybersecurity Built for the Way Africa Gets Attacked.
What does the latest KE-CIRT/CC report show about cyber threats in Kenya?
KE-CIRT/CC reporting shows large volumes of detected threat events across categories such as malware and web-application attacks. Detected events are not the same as successful breaches, and the figures do not identify one universal entry route for every organisation. 912 therefore scopes controls across identity, endpoints, networks, and the perimeter.
Do you offer incident response for ransomware attacks already in progress?
Yes. 912 takes emergency incident-response engagements: we triage, contain, and invoice only on agreed engagement scope. We have recovered an enterprise mid-crisis with full data restoration and rebuilt operating documentation — see the Senegal Factory Rescue case study. Response logistics are confirmed at first contact based on your location and the state of your backups.
Is 912 compliant with the Kenya Data Protection Act 2019?
The Data Protection Act applies to how each organisation collects, uses, protects, retains, and reports personal data. 912 can scope technical controls, data-flow documentation, incident records, and remediation support, but a product or vendor cannot guarantee compliance. Legal duties and reportability decisions remain with the controller or processor and its advisers.
What does 912's security monitoring actually cover?
Endpoint protection alerts, identity events (Active Directory/Azure AD), network telemetry (FortiGate/FortiAnalyzer), email threats, brute-force and port-scan log analysis, Geo-IP blocking, and physical security correlation (CCTV + access) where deployed. Coverage hours and response expectations are set by your Security Shield tier — Basic, Standard, or Premium — and put in writing as part of the retainer.
How much does enterprise cybersecurity cost?
Cost depends on endpoint count, licence edition and add-ons, firewall capacity, implementation scope, monitoring window, reporting cadence, and response responsibilities. The GravityZone licence component starts from KES 1,800 + VAT per endpoint per year for a minimum 15-endpoint paid deployment, but it is bundled into a managed-service quote and is not the complete service price.
Do you do penetration testing?
Yes — internal, external, and web-app penetration testing with a written report and a prioritised, budgeted remediation plan. Scope and duration are agreed per engagement based on the size of the estate and the systems in play.
Where do you operate?
Cybersecurity services across Kenya and cross-border engagements in the wider region, with delivery led from our Nairobi headquarters.
Related Technical Protocol
Try Bitdefender GravityZone Free for 30 Days: What Your Business Should Test.
A free product trial should answer whether GravityZone fits your devices, applications, policies, reporting needs, and operating team. Here is what organisations with at least 15 endpoints should test during the 30-day evaluation.
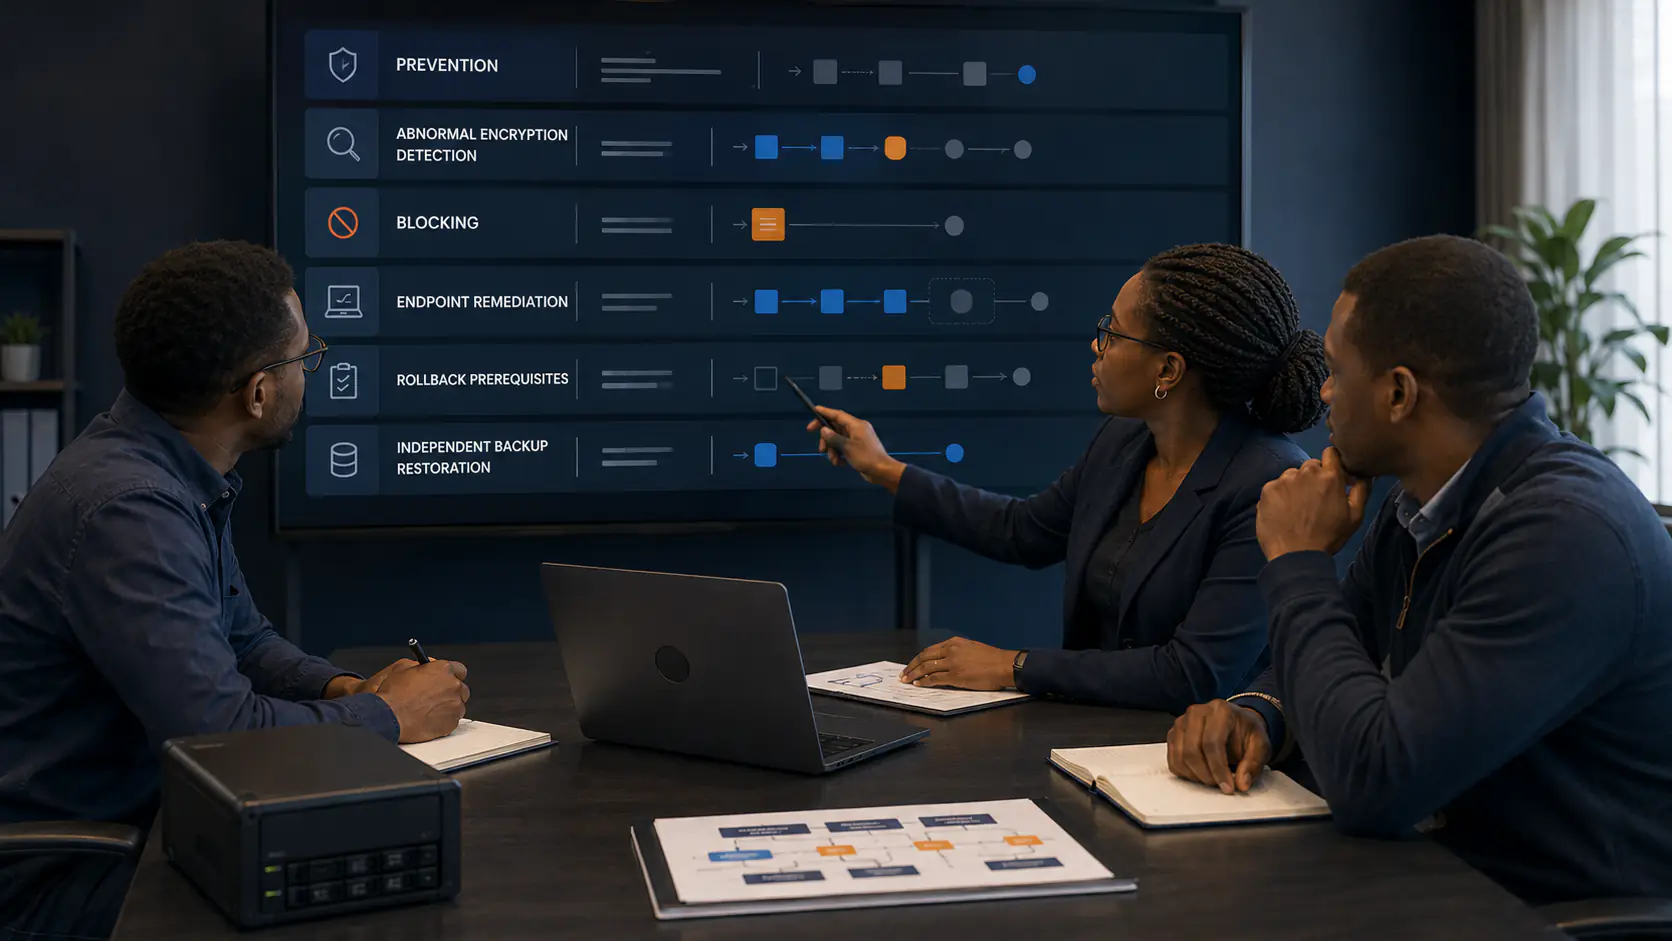
What Happens When Ransomware Starts Encrypting Files? GravityZone Prevention and Recovery Explained.
When ransomware begins abnormal encryption, GravityZone can detect the behaviour, block the responsible process, and preserve temporary recovery data where the required protection and prerequisites are active. Here is what that does—and does not—mean for recovery.
SAP ECC to S/4HANA: The 2027 Deadline Explained for Kenyan Businesses
SAP ends mainstream support for ECC at the end of 2027. Here is what the deadline actually means for Kenyan businesses, the migration paths to S/4HANA, and why planning now is cheaper than reacting later.